Network Segmentation
Firewall rules, VLAN design, and access paths reviewed so critical systems are not exposed on flat networks.
DSS designs network boundaries, identity controls, and data protection practices that match how your teams connect, share files, and run applications.
Review your network posture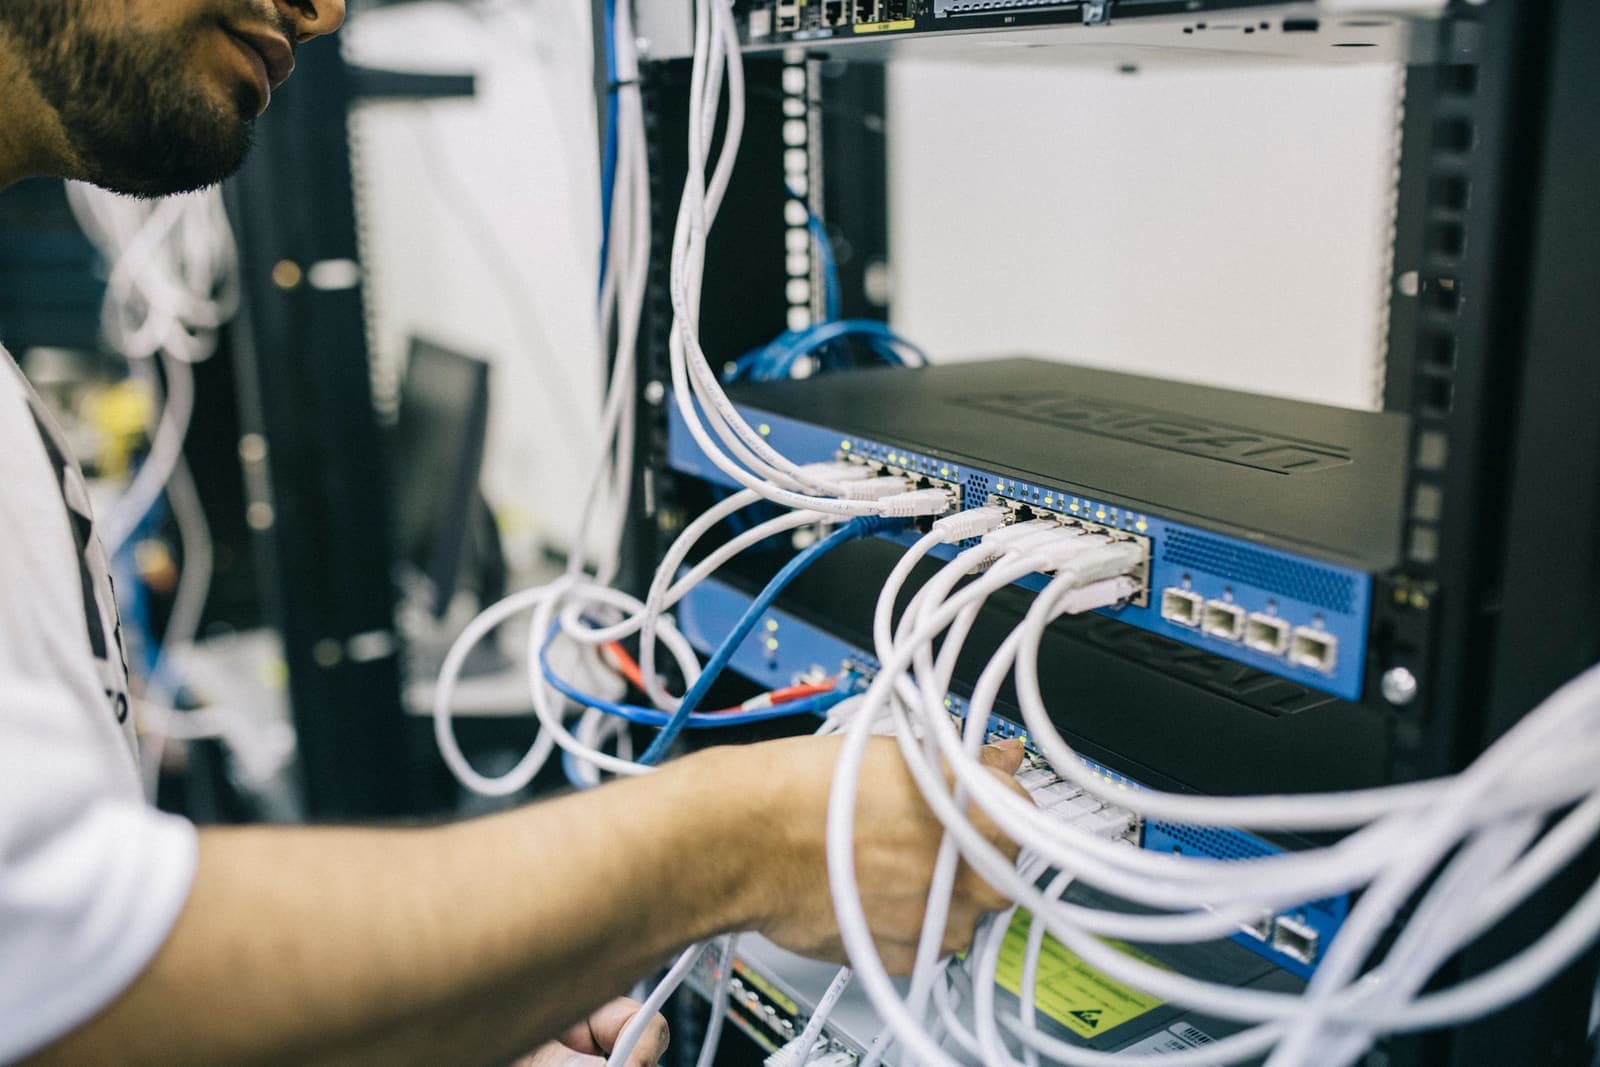
Firewall rules, VLAN design, and access paths reviewed so critical systems are not exposed on flat networks.
MFA, least-privilege policies, and remote access hardened around the accounts that reach your environment daily.
Encryption standards, sharing policies, and backup visibility aligned to the files and databases your business relies on.
We map how users, devices, and cloud services connect, then close the gaps that create unnecessary exposure.
Security improvements are prioritized for impact and usability so teams keep working while the environment gets stronger.
The questions we get asked most on a first call. If yours is not here, ask us directly.
Segmentation, access control, encryption in transit and at rest, and continuous monitoring of network and cloud signals — the controls that decide how far an intruder can move once they are past the perimeter.
Yes. Secure remote access to files and resources is a standard part of the work, and it is one of the areas we are asked about most by government and multi-office clients.
Our Director of Technology is HIPAA trained and we support regulated clients in healthcare and the public sector, so controls and documentation are built with an audit in mind.
Tell us what you are running now — the systems, the headcount, the problems that keep coming back. You will get a real scope and a number, not a discovery call.